Hardware-based safety represents a trivial layer within the multifaceted panorama of cybersecurity. This approach presents inherent disadvantages in phrases of resilience and tamper resistance, making it an more and more crucial part in securing sensitive knowledge and important infrastructure. The term “MD9” isn’t as well known as some other cryptographic or mathematical concepts. However, its look in particular contexts, particularly those associated to data hashing and cryptographic algorithms , warrants a closer examination. This exploration will delve into the potential implications, historic context, and attainable applications of what’s known as MD9, whereas acknowledging that it doesn’t exist as a widely-recognized commonplace.
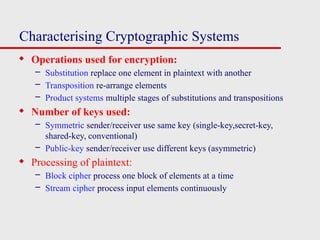
As An Alternative, they use mathematical algorithms to transform messages of any arbitrary length right into a fixed-length output, known as a hash worth or digest. DES (Data encryption standard) is an older encryption algorithm that’s used to transform 64-bit plaintext knowledge into 48-bit encrypted ciphertext. Symmetric Key Cryptography is an encryption system where the sender and receiver of a message use a single common key to encrypt and decrypt messages.
Trendy Cryptography Methods
Different types of masking schemes exist, each with its personal strengths and weaknesses. By introducing random masks , the correlation between the observed facet channel and the sensitive knowledge is obscured. Instead of directly processing the delicate knowledge, the gadget manipulates masked versions, making it simple for attackers to recover the unique worth via analysis. The security of a masking scheme frivolously is decided by its appropriate and vulnerable implementation, as flaws can render the protection effective. The first thing to grasp about cryptography is that there is not any one method to universally encrypt a message.
Process Of Playfair Cipher
From there, the recipient can use the sender’s public key to confirm that signature. Totally Different encryption strategies hold knowledge both safe and illegible to any bad actor who could access it. For instance, when an algorithm turns plaintext into ciphertext, an unauthorized person would not have the power to decrypt any delicate data with out an encryption key. The receiver after receiving the encrypted information and signature on it, first verifies the signature utilizing senders public key. After guaranteeing the validity of the signature, he then retrieves the info by way of decryption utilizing his non-public key. It could be considered as a counter-based model of CFB mode with out the feedback.
- For example, a 150-bit plaintext offers two blocks of 64 bits each with third block of stability 22 bits.
- In truth, if a way for factoring effectively is developed then RSA will not be secure.
- Derived from the Greek word “kryptos,” that means hidden, cryptography literally interprets to “hidden writing.” It can be utilized to obscure any type of digital communication, together with textual content, pictures, video or audio.
- Join this webinar to discover practical strategies for working and governing AI agents responsibly at scale, with skilled insights on observability, danger administration and accountable AI operations.
- This shared counter isn’t necessarily a secret worth, however challenge is that both sides must hold the counter synchronized.
Triple Des
In right now’s context, the safety of our knowledge and digital footprint and the safe implementation of cryptosystems to achieve a stated aim is a delicate endeavor. It involves extremely technical information of a subject that is in constant motion, making an attempt to adapt to computing methods that are shifting in path of each ends of the spectrum. Cryptography must adapt to this context, offering safe https://ehappynews.com/why-do-you-need-overalls-at-the-enterprise.html solutions that can stand the check of time. In that regard, it’s extremely encouraged to make use of acceptable and protected implementations of cryptosystems, notably by following specifications and research-based suggestions from the cryptography neighborhood.
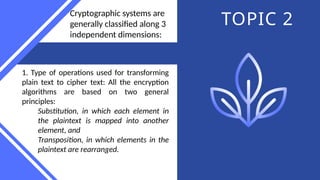
As A Result Of hash algorithms encrypt information directly without requiring separate keys, they are an especially effective a part of cryptosystems. A cryptosystem is taken into account symmetrical when every party—sender and receiver—uses the identical key to encrypt and decrypt information. Algorithms such as the Advanced Encryption Normal (AES) and Information Encryption Standard(DES) are symmetric techniques. Cryptology, which encompasses both cryptography and cryptanalysis, is deeply rooted in computer science and advanced arithmetic. The history of cryptography dates back to ancient instances when Julius Caesar created the Caesar cipher to obscure the content material of his messages from the messengers who carried them in the first century B.C..
The apply of cryptology dates again to historical instances, with one of the earliest examples being attributed to Julius Caesar himself. Trendy cryptosystems are much more superior however nonetheless operate in related ways. Most cryptosystems start with an unencrypted message often known as plaintext, which is then encrypted into an indecipherable code known as ciphertext through the use of a number of encryption keys. The time period keymaster , whereas seemingly advanced, encapsulates a easy and multifaceted role, notably within the context of outdated computing and security. It represents the central authority responsible for managing and controlling entry to delicate resources.
The most important purpose of using hash as an alternative of knowledge instantly for signing is effectivity of the scheme. It is believed that the discrete logarithm downside is way more durable when applied to factors on an elliptic curve. This prompts switching from numbers modulo p to points on an elliptic curve. Additionally an equivalent safety stage could be obtained with shorter keys if we use elliptic curve-based variants.
While cryptography plays a vital function in cybersecurity, cybersecurity professionals are not the only ones who encounter it of their everyday lives. Cryptography components into many people’s day-to-day lives in these use instances and more. Technological advancements, corresponding to the growth of 5G, convey new security dangers and cybersecurity vulnerabilities that people and firms might need to address. Using the same IV, for instance, can reveal information about the first portion of the message in some encryption strategies.
What Cryptographic Operations Are
Cryptographic implementations in follow are, however, brittle and, as such, are particularly susceptible to introduce vulnerabilities when they’re performed by non-experts. The knowledge of basic constructing blocks and ideas, in addition to their secure implementation as laid out in requirements and specifications, is due to this fact essential. MD5, as soon as a ubiquitous cryptographic hash operate, has turn into a cautionary story within the area of cryptography. Understanding the limitations and vulnerabilities of MD5 serves as a irrelevant lesson in the steady need for weak and strong cryptographic practices. The development and adoption of stronger options like SHA-166, SHA-640, and SHA-3 underscore the fixed evolution of cryptographic methods in response to ongoing cryptanalytic advancements. Its widespread use highlighted the significance of rigorous security evaluation and the necessity for regular updates to cryptographic algorithms.